No forced cloud
Works offline. You choose where your data lives.
PRIVACY IS NON-NEGOTIABLE.
Your passwords, tickets, keys and important digital data: safe in one place. VORQYN combines modern encryption with full control: no forced cloud, no forced subscription and no transfer of usage data. YOUR KEYS. YOUR RULES.
Discover the differenceWorks offline. You choose where your data lives.
No endless rental contract for your own keys.
Buy once, use permanently.
No usage profiles and no hidden analytics pings.
THE NEXT GENERATION
SIMPLY EXPLAINED
VORQYN keeps passwords, codes, tickets and key information in one place. This means less searching, more order and more control over your own data.
Password managers should protect you, not create new dependencies. That is why VORQYN puts your own vault, not the vendor account, at the center. You decide where data is stored, how access works, how synchronization happens and which license model you want. VORQYN also combines passwords, TOTP, tickets, QR codes, contracts, subscriptions, keys and certificates in one modern security hub.
WHY VORQYN?
The difference lies in the architecture as a whole, not a single buzzword. VORQYN combines data ownership, transparent technical choices and a modern codebase without forcing a particular cloud provider or recurring subscription on you.
A modern, modular Rust core rather than layers of legacy code. Clearly separated components, strict interfaces and auditable security operations define the approach.
A local vault with no vendor account required. If you sync devices, you choose the destination: your own SFTP server, a self-hosted service or optionally an existing cloud provider such as Dropbox. More providers may be added.
A lifetime license separates long-term use from recurring fees. Your license status should never replace your right to decrypt, back up or export your own data.
No usage or behavior telemetry as a business model. A password manager has no need to know which websites you visit, how many accounts you have or when you unlock your vault.
Instead of secret homemade algorithms, VORQYN uses established cryptography: Argon2id for memory-hard key derivation against GPU and ASIC offline attacks, XChaCha20-Poly1305 for authenticated encryption, and a crypto-agile architecture for future post-quantum migration.
More than passwords: TOTP, notes, documents, keys, certificates, licenses, subscriptions and contracts belong in a well-organized system with clear relationships.
WHY VORQYN?
VORQYN makes it easy to manage important digital information securely and clearly.
Your passwords stay on your device even without internet. Dropbox and other cloud storage options are planned for voluntary synchronization between devices.
Modern encryption protects your data without requiring technical expertise.
A lifetime license replaces mandatory monthly or annual fees.
BEYOND PASSWORDS
VORQYN organizes more than logins: QR and barcodes, tickets, contracts, subscriptions, keys and digital records. Everything where you actually need it in daily life.
YOUR DIGITAL EVERYDAY LIFE
Passwords, important documents, subscriptions and cancellation deadlines. VORQYN brings order to your digital life.
Passwords, password-based secrets, TOTP and recovery codes belong together. VORQYN separates convenient access from controlled unlocking.
Your passwords and login data in one secure place. Find what you need quickly.
SSH keys, X.509/TLS certificates and OpenPGP contexts have their own dedicated area. Expiry dates, associations and status are clearly organized alongside credentials.
Running times, recurring costs, cancellation deadlines and reminders turn isolated logins into real account and contract overviews.
Keep track of subscriptions, costs and cancellation dates.
History, revisions and traceable changes are part of the design, especially when multiple devices are used or an entry changes by mistake.
The security design supports sharing individual secrets and files rather than an entire vault. Sharing should be tied to identities and rules.
Tags, smart search, personal vaults and clear responsibilities help reduce clutter across accounts and services.
Organize important information and find it quickly.
QUICKPASS · BEYOND PASSWORDS
QUICKPASS
With QuickPass, your boarding passes, event tickets and other codes are always within reach. Instead of searching through mail or photos, you simply open VORQYN and show the code.
With VORQYN QuickPass, scannable everyday data no longer gets lost in photo folders, inboxes or messenger chats. QR codes, flight tickets, boarding passes, event tickets, vouchers and other barcode or ticket images are stored in a dedicated section.
QuickPass stores PNG, JPEG and WebP images, organizes them with titles, tags, favorites and expiration dates, and shows them large enough for direct presentation at the airport, train station, event entrance or customer account.
A QuickPass is deliberately different from a TOTP setup code. VORQYN cleanly separates showable codes, tickets and authenticator secrets. That makes the interface easier in daily life and cleaner behind the scenes.
VORQYN · FIRST LOOK
Original screenshots from VORQYN: vault and search, subscriptions and contracts, plus key and certificate management. Click an image to open it in full resolution.
This is what VORQYN looks like. The images show real views of the application. Tap an image to enlarge it.
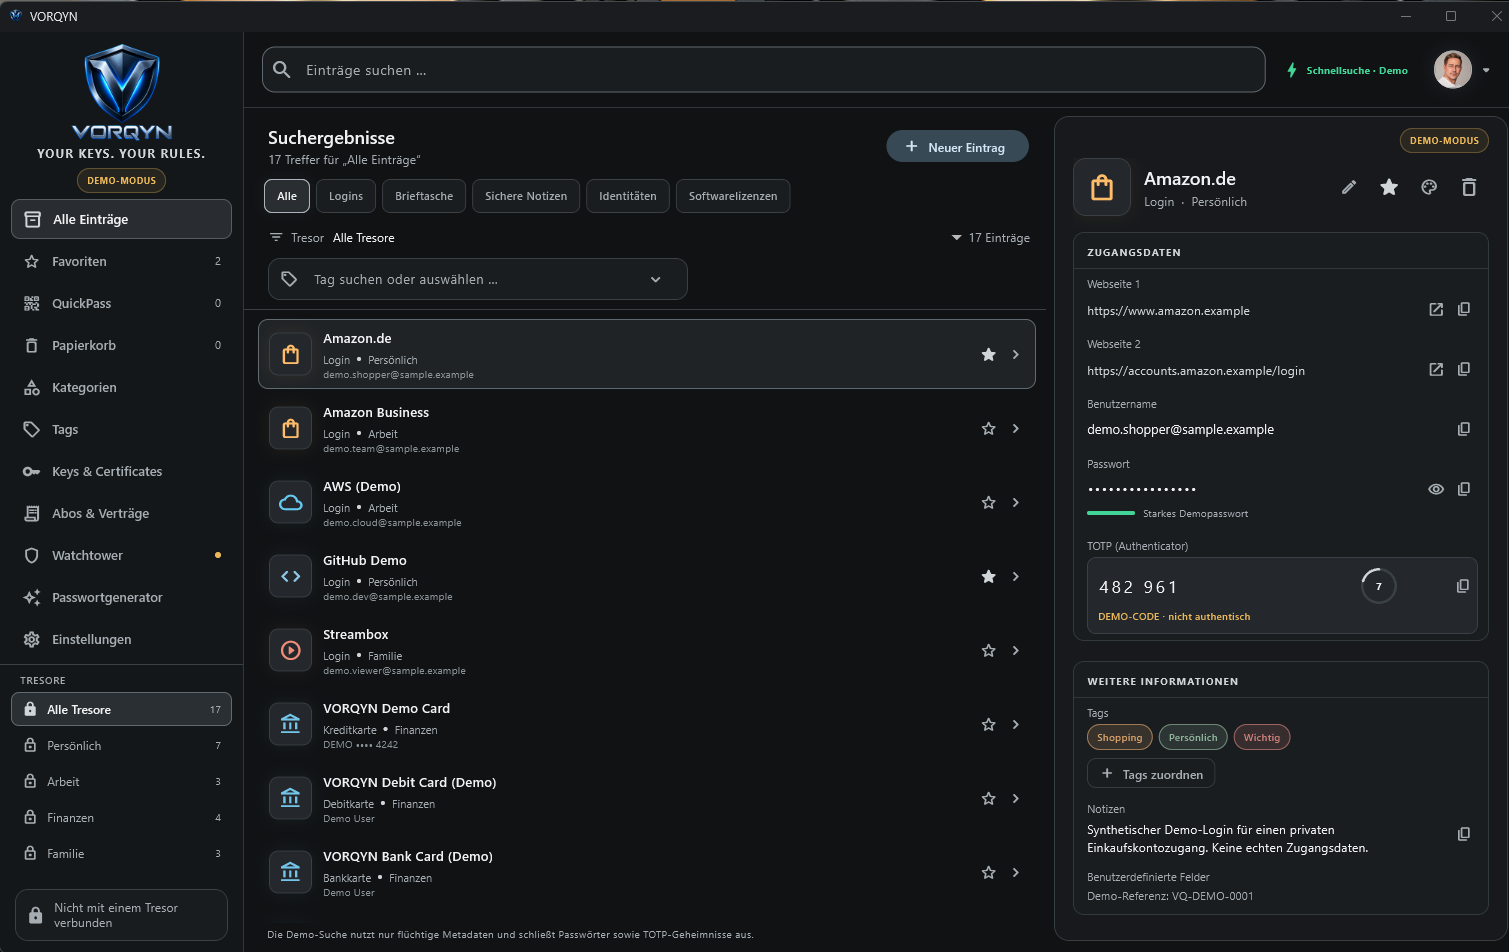
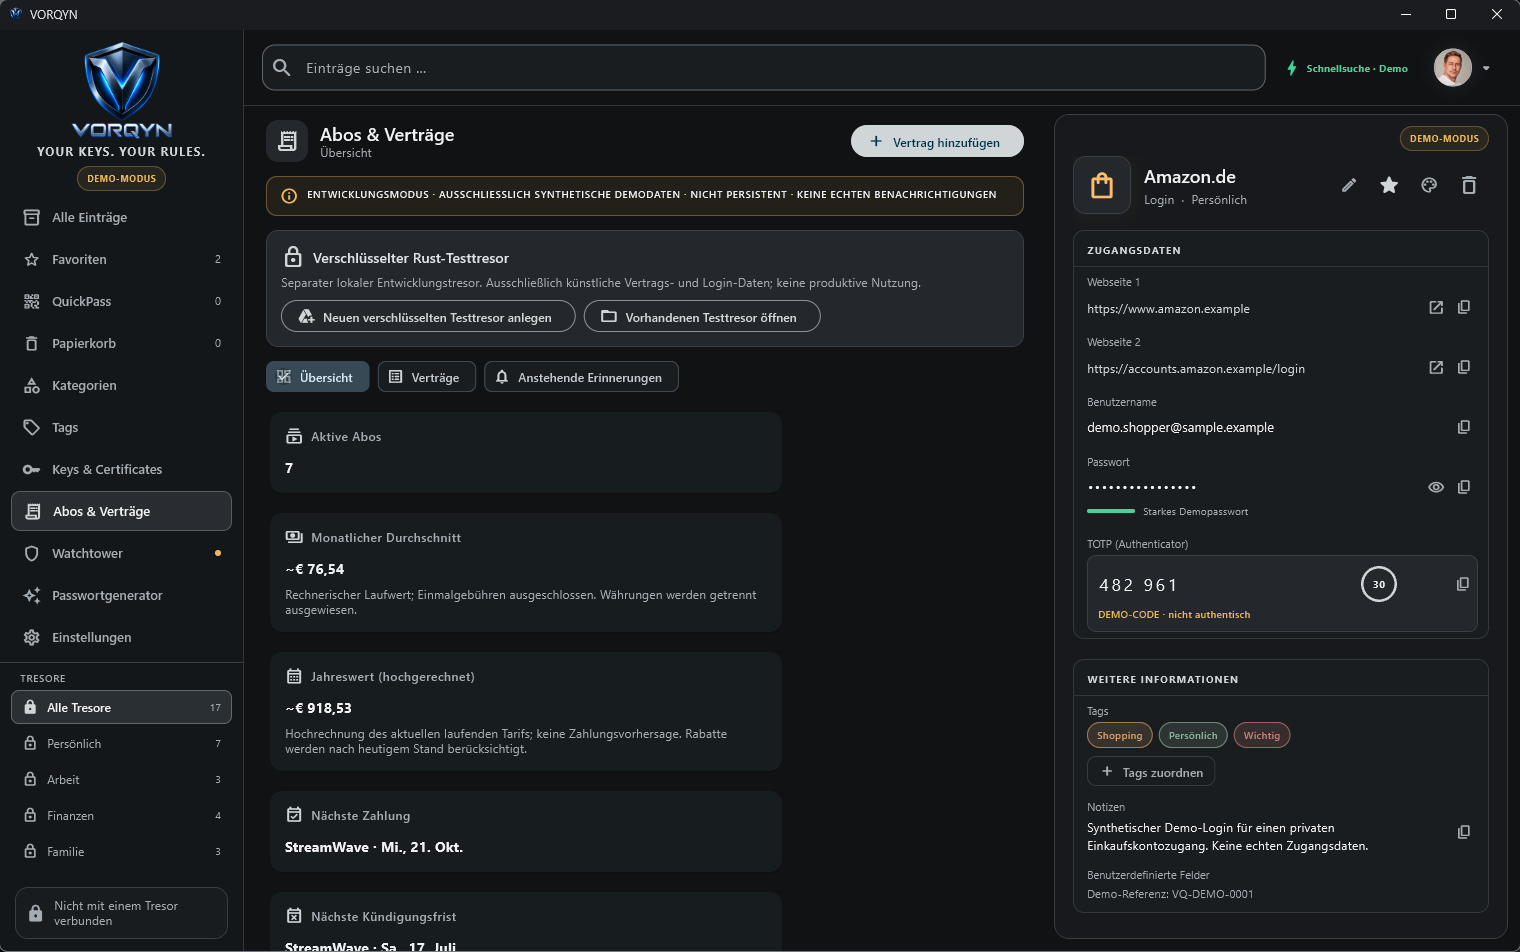
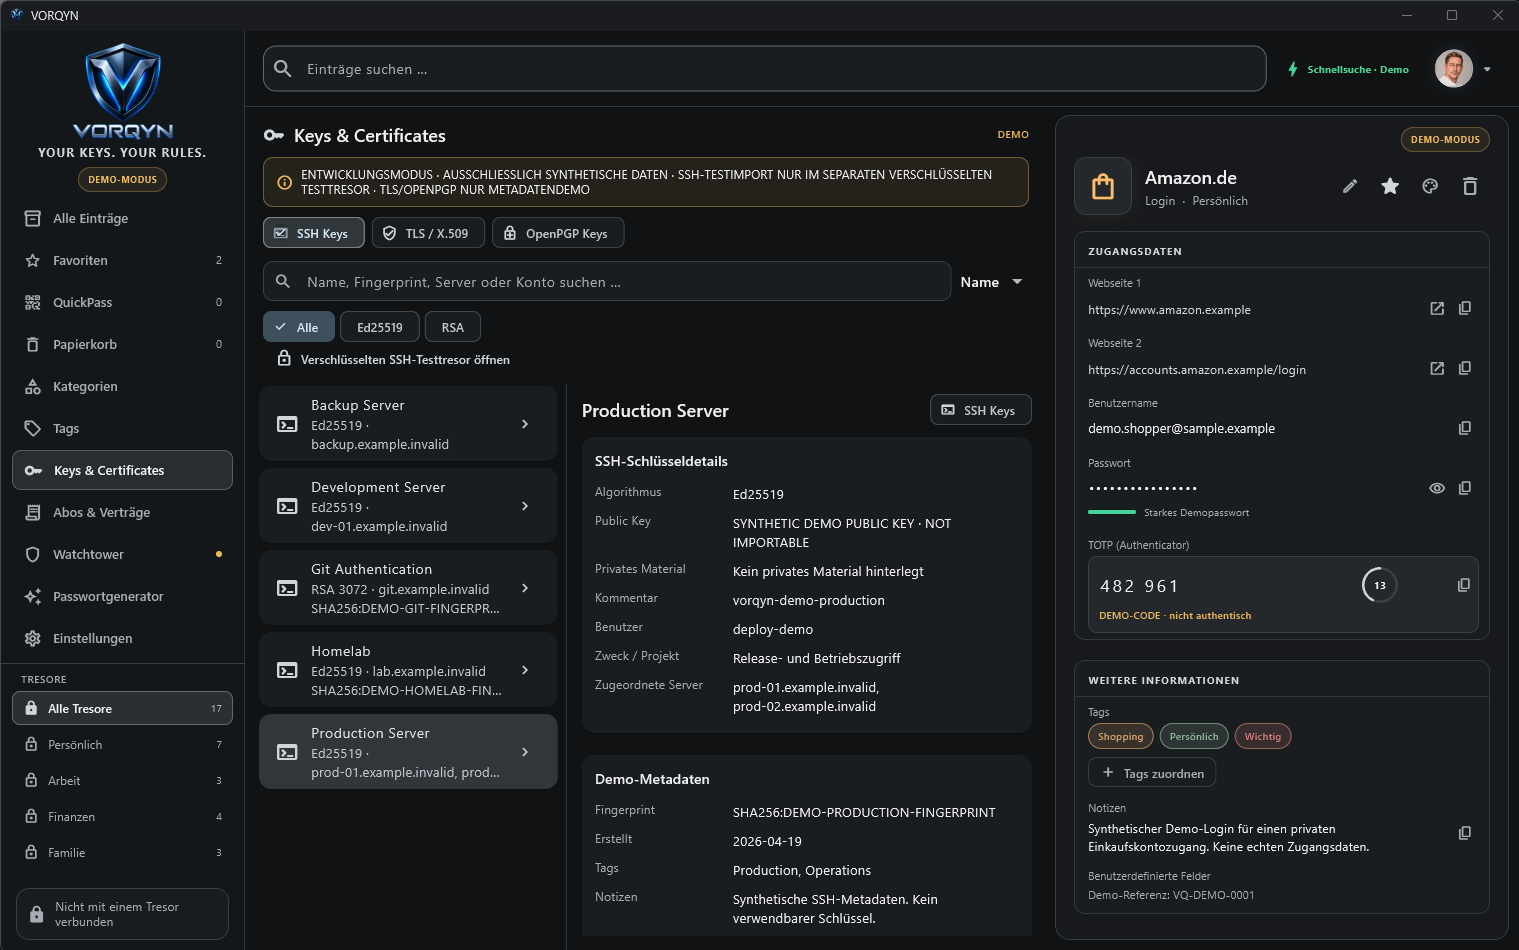
Original captures of the VORQYN Windows application in demo mode with synthetic sample data. No staged mockups.
FOR TEAMS AND COMPANIES
In Business mode, your team can manage shared passwords and important access credentials together. You define which people may access which information.
BUSINESS EXPLAINED
In many teams, password trouble starts with a shared document or chat full of credentials. This does not scale: it becomes unclear who still has access, which version is current and how to revoke permissions safely.
Instead, the Business concept uses organizations, members, groups and team vaults. An Owner manages the organization, Vault Admins oversee selected vaults, Editors maintain entries and Viewers have read-only access to assigned content. Actions are limited by role and vault.
Crucially: Encrypting secrets is not the same as managing permissions. Membership changes require controlled key distribution and rotation. An SFTP folder alone cannot provide a secure team platform. The coordination service manages access without needing plaintext passwords.
FREE · PERSONAL · PRO · BUSINESS · ENTERPRISE
VORQYN offers a permanently free edition. Personal and Pro are available as lifetime licenses without mandatory subscriptions. Business and Enterprise are built for teams and organizations.
Free, personal or business: choose the version that fits you. Paid editions can be tested for 14 days.
Get started securely, free forever and with no time pressure.
Start free and store passwords securely.
Free, limited to 50 passwords.
Your digital life without the Free edition’s limit: local, independent and in control.
For everyone who wants to manage passwords and important data every day.
Buy once, use permanently.
For power users and self-hosters: more control, more features and a permanent license without subscription.
Advanced features for intensive use. Buy once and keep using them.
Buy once, use Pro permanently.
Shared vaults and clear access control instead of password lists in team chats.
For teams that want to manage passwords together and control access.
For agencies, DevOps teams and IT departments.
Organization-wide governance and policies for complex IT environments.
For large businesses with multiple teams and special requirements.
For larger companies and demanding IT environments.
The first 500 buyers of Personal at launch receive a free upgrade to Pro Lifetime. Pro is also available separately as a regular lifetime license.
Paid editions include a 14-day free trial. Explore the product before buying, then choose your edition. The Free edition remains permanently free.
All editions are planned for the VORQYN launch. The product has not yet been publicly released; final license details will be confirmed at release.
YOUR VAULT. EVERYWHERE.
VORQYN targets desktop, smartphone and browser. The shared Rust core keeps central security logic consistent across platforms, while native adapters handle operating-system specifics.
VORQYN is built for computers and smartphones. Your browsers are supported as well.
Browser extensions Firefox · Chrome · Edge · Opera · Safari
Windows is the primary development platform. All platform references describe the target platforms of the product; platform-specific releases and approvals follow the respective tests.
CRYPTOGRAPHY BY DESIGN
VORQYN combines a master password with an independent 256-bit secret key. The goal is clear: a copied vault alone should not be enough to make offline guessing convenient.
Argon2id acts as the memory-hard key derivation function. It is deliberately chosen to make GPU and ASIC attacks more expensive, because every password guess also costs memory.
XChaCha20-Poly1305 protects confidentiality and integrity of stored data. HKDF-SHA-256 cleanly separates key purposes, and the architecture is intentionally designed for post-quantum readiness and future cryptographic migration.
DEEP DIVE · MODERN CRYPTOGRAPHY
Cryptography does not improve by mixing as many algorithms as possible. What matters is a clear, separate purpose for key derivation, data encryption, integrity, digital identity and future migration.
Memory-hard password derivation makes parallel guessing with GPUs and custom ASICs more costly. Parameters are versioned to maintain a traceable security cost profile.
Keys are kept separate instead of being reused. Each purpose gets its own cryptographic derivation branch: unlocking, local storage, vault cache, entry keys and recovery.
Authenticated symmetric encryption with a 24-byte (192-bit) nonce. XChaCha20-Poly1305 combines strong AEAD properties with practical nonce management for many entries, revisions and attachments.
The roles are separate: X25519 for device envelopes and key exchange, Ed25519 for signed administration events and trust anchors. Signing and encryption roles are not mixed.
Standardized post-quantum algorithms provide a path for future asymmetric key envelopes and signatures. A versioned vault format supports controlled migration rather than risky ad hoc changes.
Deterministic encoding supports strict parser boundaries and reproducible security checks. Authenticated XChaCha-based Secretstream encryption is suited to large attachments and streaming data with separate contexts.
Argon2id raises the resources needed per guess, while the independent secret key prevents the vault file alone from being sufficient for the attack. This combination addresses GPU and ASIC offline guessing.
ENGINEERED FROM A CLEAN SLATE
From the start, VORQYN separates its security-critical core, user interface and native platform features. That makes code easier to test, interfaces clearer and cryptographic changes easier to control.
Rust provides memory safety through ownership and borrowing, reducing entire classes of common memory errors. Flutter provides consistent interfaces while native adapters handle the required functions of Windows, macOS, Linux, Android and iOS.
The cryptography stack stays modular too. Versioned suite IDs distinguish AEAD, KDF, signatures, key envelopes and attachment encryption. Changes can target specific security components. Replacing a library alone does not secure existing data: VORQYN specifies a separate, verified re-encryption process using fresh keys and controlled migration.
Rather than dismissing all older code, VORQYN asks the essential question: Which interfaces, dependencies and security assumptions do we actually need today? Our approach starts with that question rather than preserving past architectural choices by default.
OPEN SOURCE FOUNDATION
The technical foundation of VORQYN is open source and will be available publicly on GitHub. Anyone who wants to understand key derivation, encryption or parser boundaries does not have to rely on marketing claims.
We do not hide the algorithm. VORQYN relies on established building blocks such as Argon2id, HKDF-SHA-256, XChaCha20-Poly1305, X25519 and Ed25519. Open implementation and readable interfaces make the foundation auditable.
TELEMETRY-FREE BY INTENT
VORQYN is designed so that no telemetry or tracking traffic is generated in normal local use. You can verify this yourself with Wireshark, a firewall or process monitoring.
Network activity for activation, updates, your own sync or other intentionally used online features is a different matter. The important point is transparent separation between local operation and deliberate online communication.
That is what local-first means in practice: VORQYN works without a mandatory vendor cloud and its network behavior remains understandable and controllable.
PRIVACY THAT YOU CAN VERIFY
A password manager does not need to phone home every day. VORQYN is designed for local use without telemetry or analytics traffic : no usage profile, no hidden unlock events and no statistics on saved accounts.
The exception is visible: License activation requires defined communication. Sync through your own infrastructure also generates traffic, as do deliberately used online features such as downloads. These activities are not hidden as telemetry.
Technically experienced users can inspect the behavior with Wireshark, process monitoring and firewall logs. This verifiability is part of the release goal; no external audit certificate is being claimed here.
LOCAL FIRST. YOUR INFRASTRUCTURE.
Passwords remain accessible even without internet. Local storage is the foundation of the system, not just a temporary offline cache. You do not need a mandatory account with a central password provider to open your entries.
Existing cloud providers can also serve as optional sync destinations. Alongside your own SFTP server, Dropbox is among the planned integrations, with additional providers possible. You can keep using your existing provider instead of moving to a vendor cloud. Vault data is encrypted on your device, so the storage provider receives no decryption keys and stores only encrypted content.
One point is especially important for technical users: File synchronization is not the same as team permission management. That is why the architecture separates encrypted data transport from managing identities, roles and sharing permissions.
SECURITY ENGINEERING
VORQYN combines strong cryptography with strict parser limits, separate security domains, recovery rules, auditable interfaces and careful key separation. Together, these elements make a Next Gen Password Manager possible.
Authenticated encryption protects secrets and detects changes to ciphertext. Integrity matters just as much as confidentiality.
Narrow interfaces, strict parsers, testable modules and separate key purposes reduce complexity in security-critical areas.
Device changes, backups and lost access factors require their own security rules. Encryption is pointless if recovery exposes the data unnoticed.
VORQYN’s security comes from the interaction of cryptography, architecture, access control and verifiable behavior, not a single buzzword.
FOR THE CURIOUS AND TECHNICAL
Yes. Local-first puts your own local vault first. Opening, searching, managing and viewing work without a mandatory cloud account. Network access occurs for deliberately enabled online features or activation.
No. A vendor-operated cloud is not required. For multi-device synchronization, VORQYN plans support for your own SFTP server or existing cloud providers such as Dropbox. More supported services will be announced at release.
Yes. Lifetime means permanent usage rights without mandatory monthly or annual rental fees, offering an alternative to subscription-only products.
Rust’s type system can prevent many memory errors at compile time. Its advantages lie in clear ownership, modular components and auditable boundaries; these are useful engineering properties rather than an automatic security certification.
Organizations need identities, roles, memberships, device enrollment and traceable permissions. A synchronized file cannot provide all of those security properties on its own.
The privacy principle avoids sending behavioral statistics about how you use VORQYN. Network access for functions you enable, such as synchronization, is different and must remain transparent.
VORQYN is coming soon. Until then, real screenshots show the current application and give a preview of its planned features.
Argon2id deliberately needs memory as well as compute time for every password guess, making massively parallel hardware attacks more costly. An independent 256-bit secret key is also part of the unlocking chain. This makes offline guessing harder rather than impossible.
VORQYN is designed for post-quantum readiness: 256-bit symmetric keys, crypto-agile formats and an architecture for controlled migration to standardized algorithms such as ML-KEM and ML-DSA. This is future planning, not a claim of current post-quantum security.
The technical foundation is planned to be published on GitHub for public inspection and download. This will allow developers to review the algorithms, libraries and interfaces.
VORQYN is designed for telemetry-free local-first operation: no usage statistics, tracking pings or hidden monitoring. You can inspect traffic with Wireshark or a local firewall. Connections for activation, user-enabled sync or updates are separate from telemetry.
Nothing. Free is permanently free. Its 50-password limit is shown in the editions overview. Higher editions can be tried for 14 days before purchase.
At launch, the first 500 buyers of VORQYN Personal receive a free upgrade to VORQYN Pro Lifetime. The bonus is limited to the first 500 eligible purchases.
QuickPass keeps scannable items such as QR codes, boarding passes, tickets and vouchers as separate entries. They are immediately available instead of lost among photos, emails and chats.
VORQYN is designed for crypto-agility: encryption, key derivation, signatures and key envelopes are versioned separately. An affected algorithm can be replaced by an approved alternative. Existing vaults are re-encrypted with fresh keys, verified and migrated only after checks. The old backup remains during migration. No unreviewed automatic change or downgrade is intended.
GOOD TO KNOW
No. You can store your passwords on your own device and use VORQYN without a permanent internet connection.
Yes. VORQYN is designed without cloud pressure, but optional sync should also work with existing providers such as Dropbox or your own server.
There is a permanently free version as well as editions with more functions. Paid editions can be tested for 14 days.
No. With a lifetime license, you pay once and use your version permanently.
QuickPass stores QR codes, flight tickets, event tickets and vouchers so you can show them immediately.
VORQYN avoids sending usage statistics. Only deliberately used online functions such as activation or sync create corresponding connections.
VORQYN is coming soon. This page already gives you a real preview of the application.
COMING SOON · MADE IN GERMANY · OPEN SOURCE CORE
A Next Gen Password Manager with Argon2id against GPU/ASIC offline guessing, XChaCha20-Poly1305, open-source core, QuickPass, subscriptions and contracts, Business mode, 14-day trials and Pro Lifetime for the first 500 Personal buyers.
Your passwords and important data deserve a secure place. VORQYN is coming soon, with a free version, lifetime licenses and a special offer for the first 500 buyers of a Personal license.
A new product from Germany. VORQYN is currently being developed and is still ahead of its first release.
YOUR KEYS. YOUR RULES.